
Tagged with
Audit
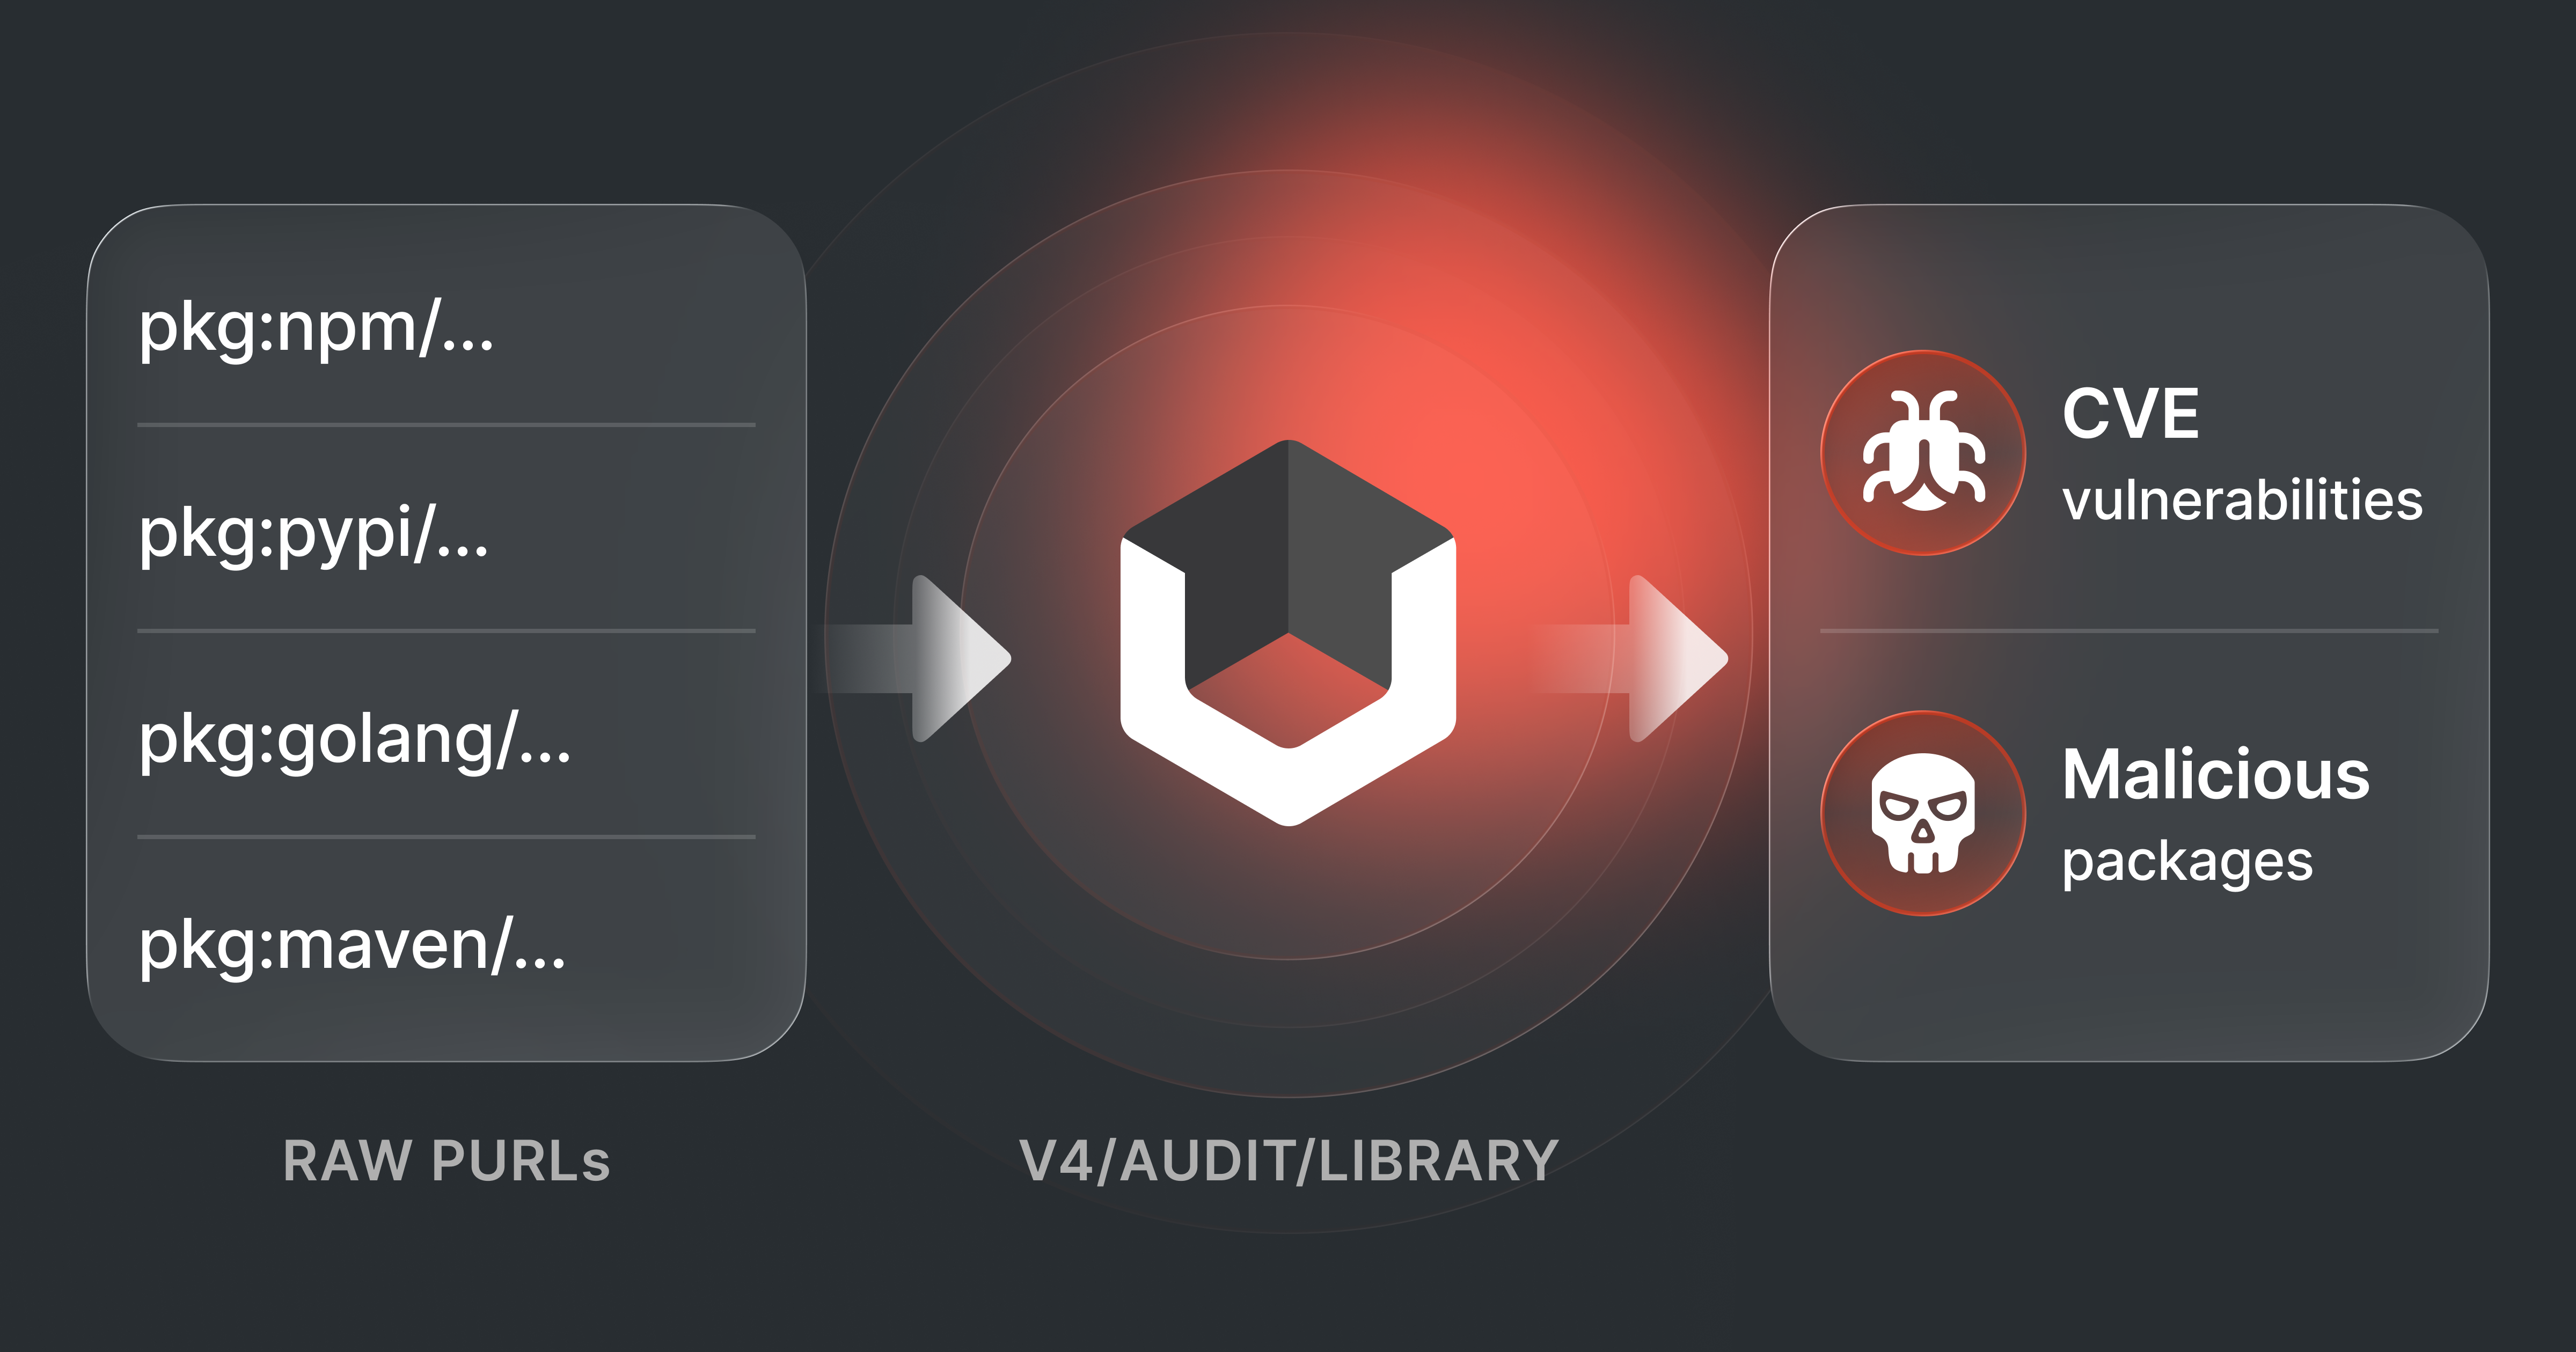
Many npm and PyPI compromises never get a CVE — the package is yanked and an OSV advisory is shipped instead. Library Audit takes raw PURLs from any ecosystem to flag CVE-tracked vulnerabilities and registry-yanked compromises before `pip install`, not the morning after.
21 May 2026
NIST moved the NVD to risk-based enrichment on April 15 — a quarter of recent CVEs now arrive Not Scheduled. Vulners has been filling the CPE gap since February 2024. Here is the four-source configuration layer and how to use it.
19 April 2026
You have an SBOM. Now what? Vulners SBOM Analyzer turns a standard SPDX or CycloneDX file into a vulnerability report enriched with CVSS, EPSS, AI Score, exploit references, and fix versions — in the browser or via a single API call.
4 March 2026
The Vulners team presents an additional auditing method for Linux CentOS distributions of ...
3 June 2021